The line, the batch,the utilities behind them.
A factory is where IT and OT met first and were never properly introduced: PLCs and robots on the line, a DCS in the process unit, MES and historians upstairs, chillers and compressors out the back, and a dozen integrators with a login each. ASTRICS gives the plant one operational understanding — every controller, what it makes, who owns it, and what stops if it fails.
India produced 168 million tonnes of crude steel in FY2025–26 and is the third-largest pharmaceutical producer by volume. Captive power at 50 MW or more inside any of these plants is in scope of the CEA cyber security regulations.
Sources: Ministry of Steel, April 2026; Press Information Bureau; CEA (Cyber Security in Power Sector) Regulations, 2026, Reg 2(1)
The plant estate,as ASTRICS reads it.
Line, process, utilities and the systems above them land in one register, each with its process, its owner and its consequence to output attached.
PLCs, drives and robots
The cell controllers and the machines they run. Discovered on the wire, grouped by line and cell, and ranked by the output behind them.
DCS and batch systems
Process control in pharma and chemicals, where the batch record is a regulated document and the recipe is intellectual property.
MES and historians
The layer that turns the plant into data — and the most common bridge between the corporate network and the line.
Safety instrumented systems
Independent layers that stop a reaction or a press safely. Their separation from control is a control in itself.
Utilities
Chillers, compressors, boilers, building management and captive power. Unglamorous, shared, and an outage in waiting.
OEM and integrator access
Machine builders, system integrators and maintenance contractors. Every session observed, attributed and checked against its window.
Why the factorygets hit first.
Manufacturing has been the most-attacked sector for ransomware for years, for a simple reason: downtime is expensive, the networks are flat, and the IT incident reaches the line faster than anyone expects.
Availability is the business
Every hour a line is down is measurable. That is why ransomware crews target manufacturers — and why consequence, not severity, has to decide what is fixed first.
Data integrity is regulated
In pharma the batch record is evidence. A controller that can be altered without trace is a compliance failure before it is a security one.
Flat cell networks
Lines commissioned by integrators over twenty years share address space, credentials and switches. Segmentation exists on the drawing; whether it exists on the wire has to be tested.
On the record
- 2020
Dr. Reddy's Laboratories isolated its data centres and shut plants worldwide after a cyber attack, days after receiving approval to trial a COVID-19 vaccine.
Dr. Reddy's stock exchange filing, October 2020
- 2023
Sun Pharmaceutical reported a ransomware attack, claimed by ALPHV/BlackCat, and warned it would reduce revenue and affect operations.
Sun Pharma stock exchange filing, March 2023
- 2019
Norsk Hydro's aluminium plants fell back to manual operation for weeks after LockerGoga ransomware; the company put the cost at around US$50 million in the first quarter alone.
Norsk Hydro quarterly report, 2019
What the rules askof a manufacturer.
Summaries of the notified text as we read it in September 2026. Orientation, not legal advice — check the Gazette before you rely on a clause.
CERT-In, six hours
IT Act s.70B(6) DirectionsThe CERT-In Directions of 28 April 2022 bind every body corporate: covered incidents reported within six hours of noticing, 180 days of ICT logs kept in India, clocks synchronised to NIC or NPL time.
Captive power in scope
CEA Regulations 2026, Reg 2(1)A captive generating plant at 50 MW or more — common in steel, cement, chemicals and refining — comes under the CEA (Cyber Security in Power Sector) Regulations, 2026 from 1 April 2027.
IEC 62443 as the Indian standard
BIS / IEC 62443The Bureau of Indian Standards has adopted the IEC 62443 series as Indian Standards. Zones, conduits and security levels are the vocabulary customers, insurers and auditors will use.
Sector rules on integrity and data
CDSCO / GMP; DPDP Act 2023Good manufacturing practice and data-integrity expectations in pharma, and the Digital Personal Data Protection Act, 2023 for personal data, sit alongside the IT Act. None of them are OT regulations; all of them fail when the controller record cannot be trusted.
to report a covered cyber incident to CERT-In after noticing it — for every body corporate, whatever the sector.
of ICT system logs to be kept, inside India, and produced to CERT-In on request.
How ASTRICS mapsto a plant.
One platform, one language, one source of truth. Understand, Govern, Protect, Orchestrate and Assure travel together, so every capability below reads the same record.
Segmentation, tested on the wire
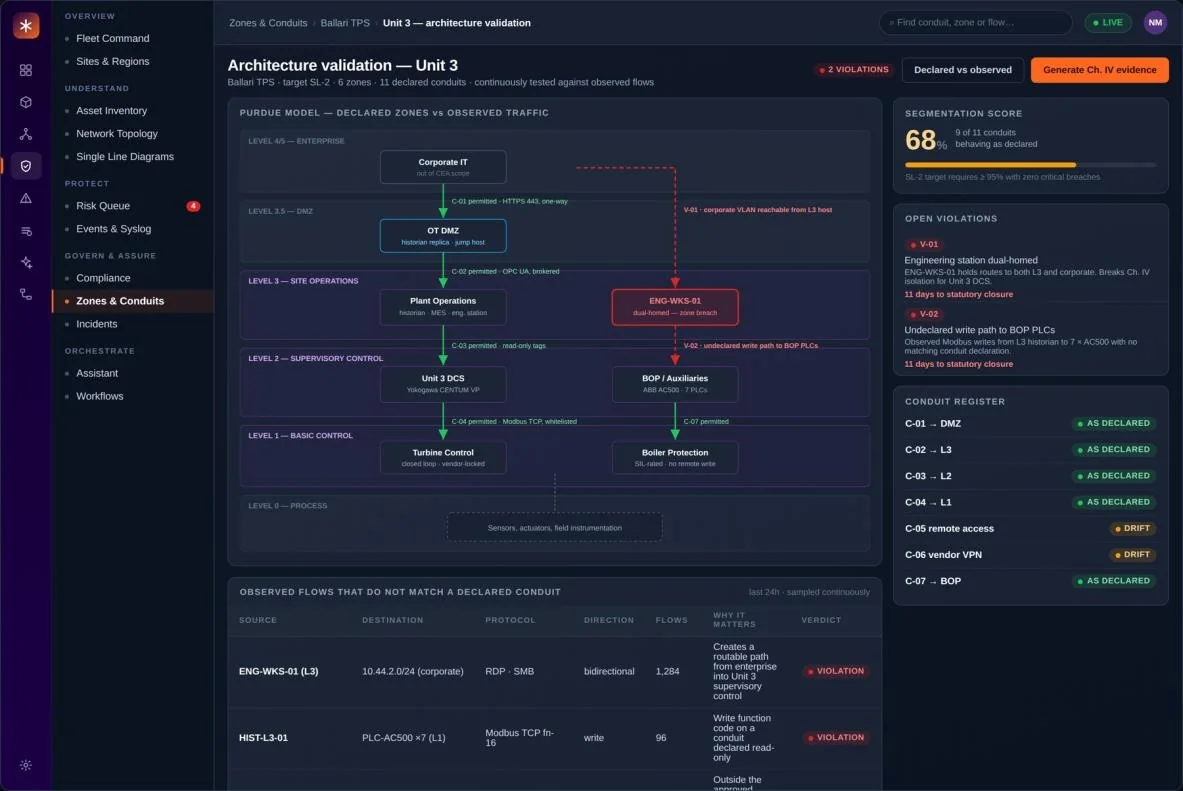
Zones & Conduits declares the cells, the lines and the boundary to the corporate network, then tests them continuously against observed traffic. A mismatch is a dated finding.
A passport for every controller
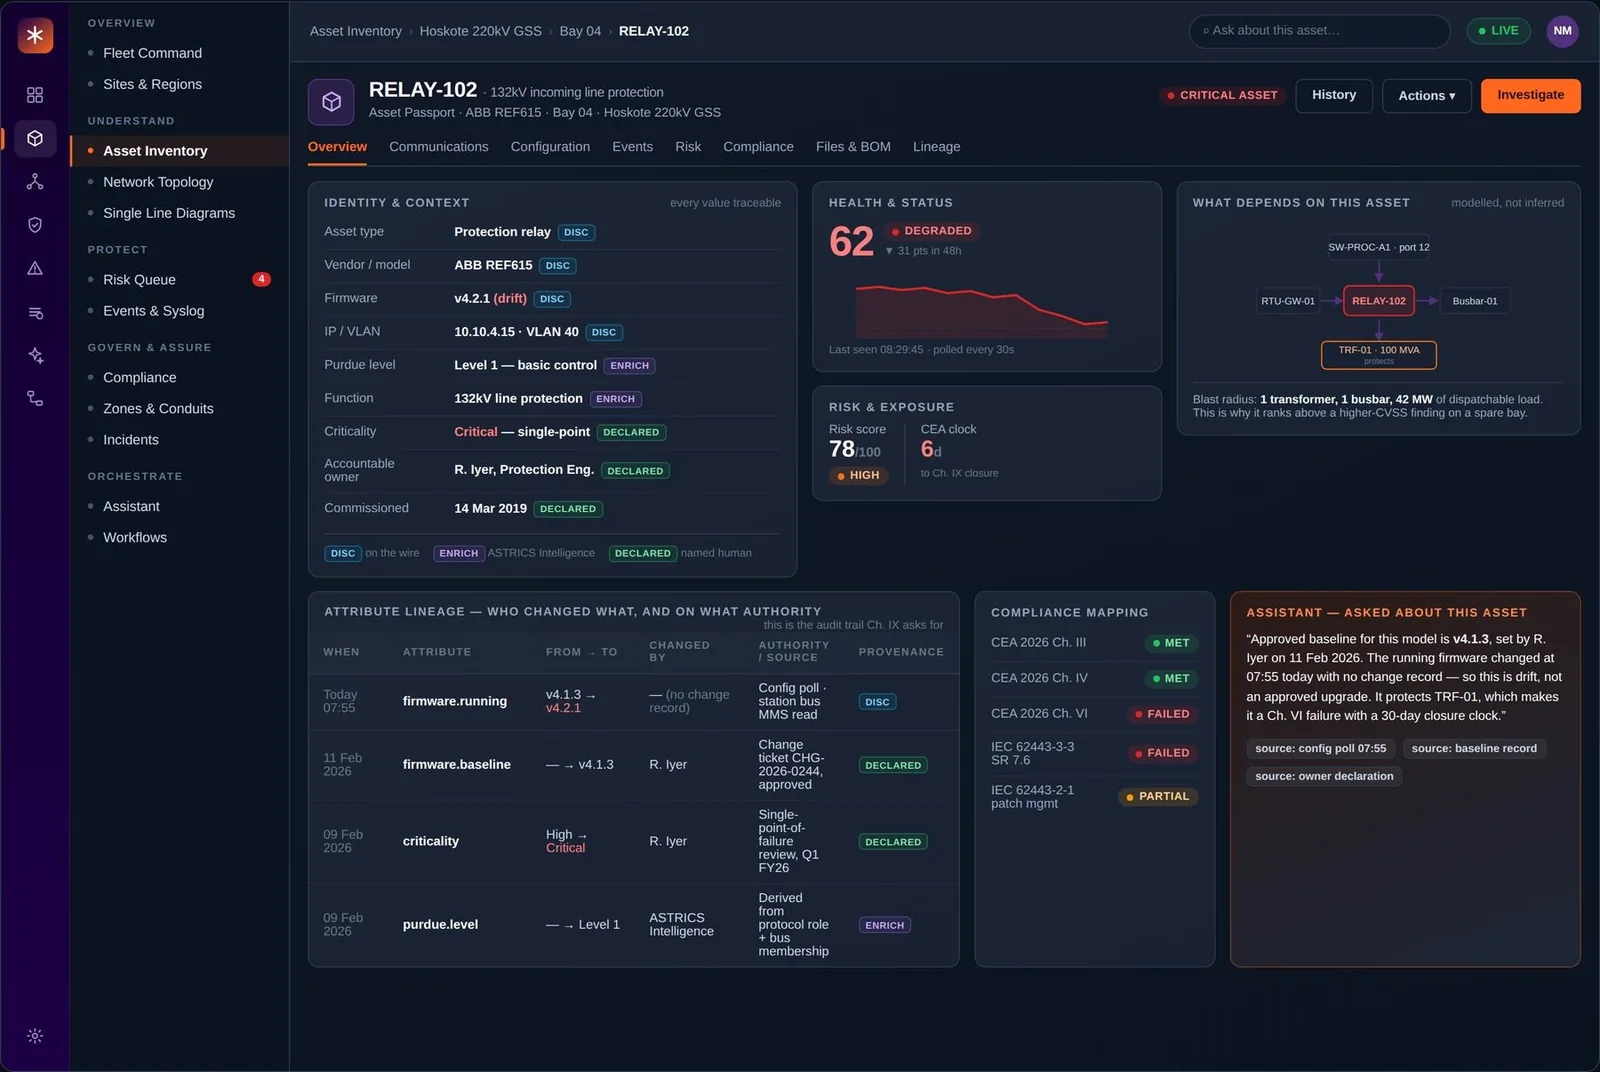
The Asset Passport holds firmware, configuration lineage and vendor access for each PLC and robot controller — the trail an integrity audit asks for.
Risk ranked by what stops
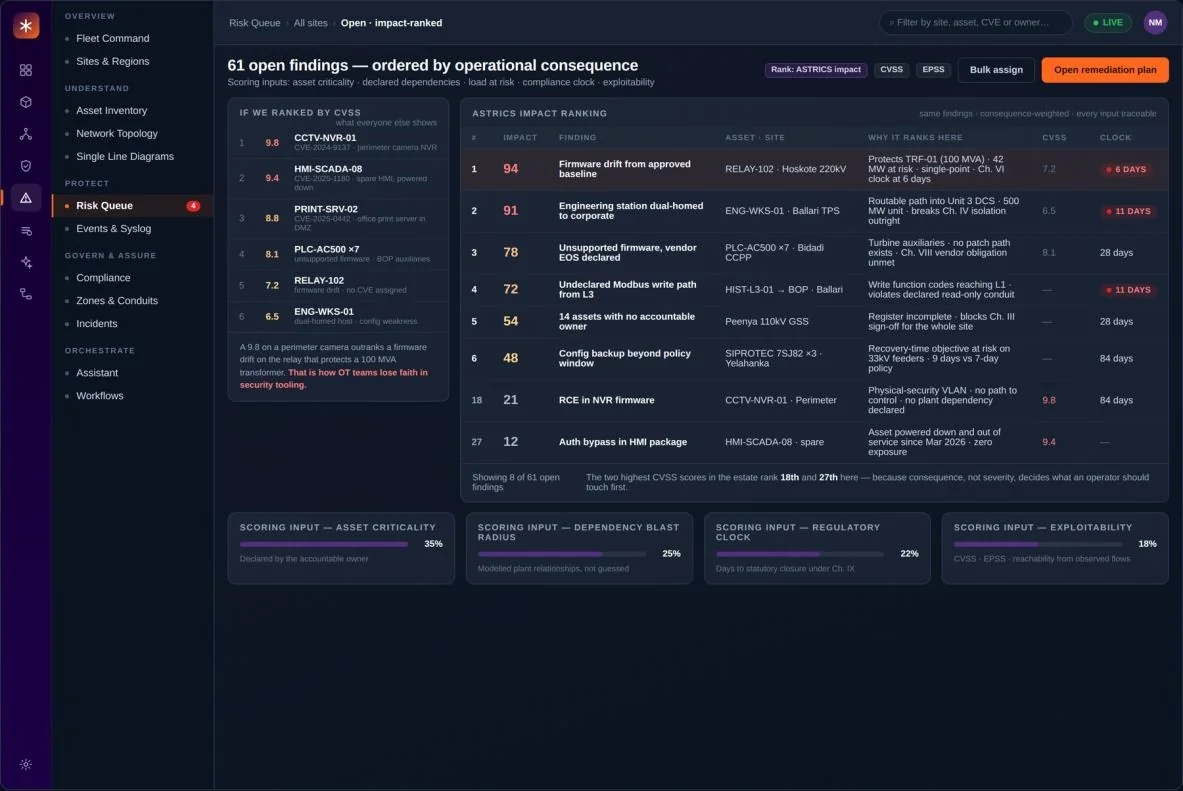
The Risk Queue orders vulnerability data by consequence to output, so the controller that stops the line ranks above the highest CVSS score in the office.
One record for many sites
Fleet Command gives one posture number per obligation across every plant, so the weakest site in the group is obvious.
Zones & Conduits
Chapter IV asks an operator to prove trust-level segmentation, not describe it. Declared zones and permitted conduits are continuously tested against observed traffic, and every mismatch becomes a dated finding.
Asset Passport
One asset's complete operational record — and every value on it carries its source, so an auditor can follow any figure back to where it came from.
Risk Queue
The same vulnerability data everyone has, ordered by what it would cost this operator. The two highest CVSS scores in the estate rank 18th and 27th here — because consequence, not severity, decides the work.
What operators askbefore they buy.
Straight answers, in the terms the regulation and the plant already use. Bring the rest to a walkthrough.
Is IEC 62443 mandatory in India?
It is not a statutory requirement for manufacturers as of September 2026, but BIS has adopted the series as Indian Standards and it is the framework customers, insurers and auditors increasingly ask for. ASTRICS declares zones, conduits and security levels in its terms and keeps the alignment through active enrichment rather than periodic review.
We have twenty integrators with remote access. Where do we start?
With the record. ASTRICS observes every remote session, attributes it to a named vendor and checks it against the window it was approved for, so the first output is a true list of who reaches what — and the Risk Queue tells you which of those paths matters most.
Does the CEA regulation apply to our captive power plant?
If it is 50 MW or more, yes, from 1 April 2027. The regulation names captive generating plants explicitly. ASTRICS models the captive plant and its switchyard alongside the process estate, with the CEA obligations tracked as a live state.
Will ASTRICS interfere with production?
No. ASTRICS builds the record from passively observed traffic and existing sources. Writes to control devices are not a permission it can be granted — that path does not exist in the product.
See ASTRICS against your own environment.
Book a walkthrough with the ASTRICS team and bring one site's worth of questions.