The grid, readone bay at a time.
A transmission licensee runs hundreds of substations with nobody in them. A DISCOM now has millions of meters that are also endpoints. The load despatch centres between them have been named targets of state-backed intrusion. ASTRICS reads all of it as one operational understanding — every relay, every RTU, every meter head-end — with the single line diagram as the security view.
India's transmission network passed 5 lakh circuit-kilometres in January 2026, and 7.24 crore smart meters were installed by June 2026. The CEA cyber security regulations apply to every transmission licensee, distribution licensee and load despatch centre, with no capacity floor.
Sources: Ministry of Power, January 2026; Lok Sabha reply, June 2026; CEA (Cyber Security in Power Sector) Regulations, 2026, Reg 2(1)
The grid estate,as ASTRICS reads it.
From the protection relay in a 400 kV bay to the meter data system in a DISCOM data centre, every asset lands in the same register with its owner, its criticality and its consequence attached.
Protection relays and IEDs
The devices that trip a line. Firmware, settings and IEC 61850 communications are part of the record, not a spreadsheet in the protection engineer's drawer.
Substation automation and RTUs
Gateways that speak IEC 60870-5-104 and DNP3 to the control centre. Each one is a bridge between the bay and the outside — modelled as exactly that.
Load despatch SCADA and EMS
The state's view of the grid. Critical by definition, and the system state actors have gone looking for.
Smart metering and AMI
Head-end systems, meter data management and prepaid platforms bring IT scale to an OT boundary. The record shows where the two meet.
Telecom and time
Fibre, PLCC, microwave and time sources. If the channel or the clock is wrong, the protection is wrong.
OEM and integrator access
Relay vendors, automation integrators and testing contractors. Every session observed, named and checked.
Why the gridis a named target.
The Indian grid is not defended against a hypothetical adversary. The intrusions have been documented, attributed and, in one case, debated in Parliament.
Unmanned by design
A substation is visited for maintenance and faults. Between visits its IEDs and gateways are reachable, patch-late and trusting of whatever speaks their protocol.
The despatch centre in the crosshairs
Load despatch centres were the target of RedEcho in 2020–21 and of a second campaign in 2022. The value to an adversary is obvious: the ability to see, and then to switch.
Convergence at the DISCOM
Prepaid metering, billing and outage management now touch the same networks as distribution SCADA. The IT incident is one hop from the feeder.
On the record
- 2021
Recorded Future reported RedEcho, a China-linked group, deploying ShadowPad into 12 Indian organisations including four of the five regional load despatch centres and two state load despatch centres. The Government of India denied any link to the October 2020 Mumbai outage.
Recorded Future Insikt Group, February 2021
- 2022
A second campaign targeted at least seven state load despatch centres in northern India near the Ladakh border, again with ShadowPad.
Recorded Future, April 2022
- 2022
Tata Power confirmed a cyber attack on its IT infrastructure; the Hive ransomware group later leaked data it claimed came from the company.
Tata Power stock exchange filing, October 2022
- 2022
Industroyer2, a successor to the malware that cut power in Kyiv in 2016, was found targeting IEC 60870-5-104 at Ukrainian high-voltage substations.
ESET and CERT-UA, April 2022
What the rules askof a licensee.
Summaries of the notified text as we read it in September 2026. Orientation, not legal advice — check the Gazette before you rely on a clause.
In scope, no threshold
Regs 1(2), 2(1)Every transmission licensee, distribution licensee and load despatch centre is in scope of the CEA (Cyber Security in Power Sector) Regulations, 2026 from 1 April 2027, for existing as well as upcoming infrastructure.
Control traffic stays in India
Reg 6(3)Control, operation and real-time data must run over a dedicated channel isolated from the internet and confined to national boundaries; cross-border exchange only through a separate system and a unidirectional gateway.
Trust levels, declared and kept
Regs 6(1), 6(6), 6(8)OT segmented into different trust levels by criticality, security requirements and risk assessment; OT communications isolated from IT; physical isolation from the internet.
Protected systems
Reg 5(29)Provide NCIIPC with the information to identify critical information infrastructure, and apply within sixty days of identification for the asset to be notified as a protected system under the IT Act.
New critical systems reported
Regs 5(27), 5(28)Details of every new or replaced critical system go to CSIRT-Power within thirty days of commissioning, after a pre-commissioning vulnerability assessment and penetration test.
Six hours, one month
Regs 7(3)(a), 5(22), 13(3)Incidents reported to CSIRT-Power and CERT-In within six hours; audits every nine to fifteen months; critical and high findings closed within a month.
to report a cyber security incident to CSIRT-Power and CERT-In. Twenty-four hours where an incident is concluded as cyber sabotage in a critical system. (Reg 7(3)(a))
to address every critical and high-risk finding from the date the auditor submits the report; three months for medium and low. (Reg 13(3))
from NCIIPC identifying an asset as critical information infrastructure to apply for it to be notified as a protected system. (Reg 5(29))
How ASTRICS mapsto a transmission or distribution estate.
One platform, one language, one source of truth. Understand, Govern, Protect, Orchestrate and Assure travel together, so every capability below reads the same record.
The single line diagram as the security view
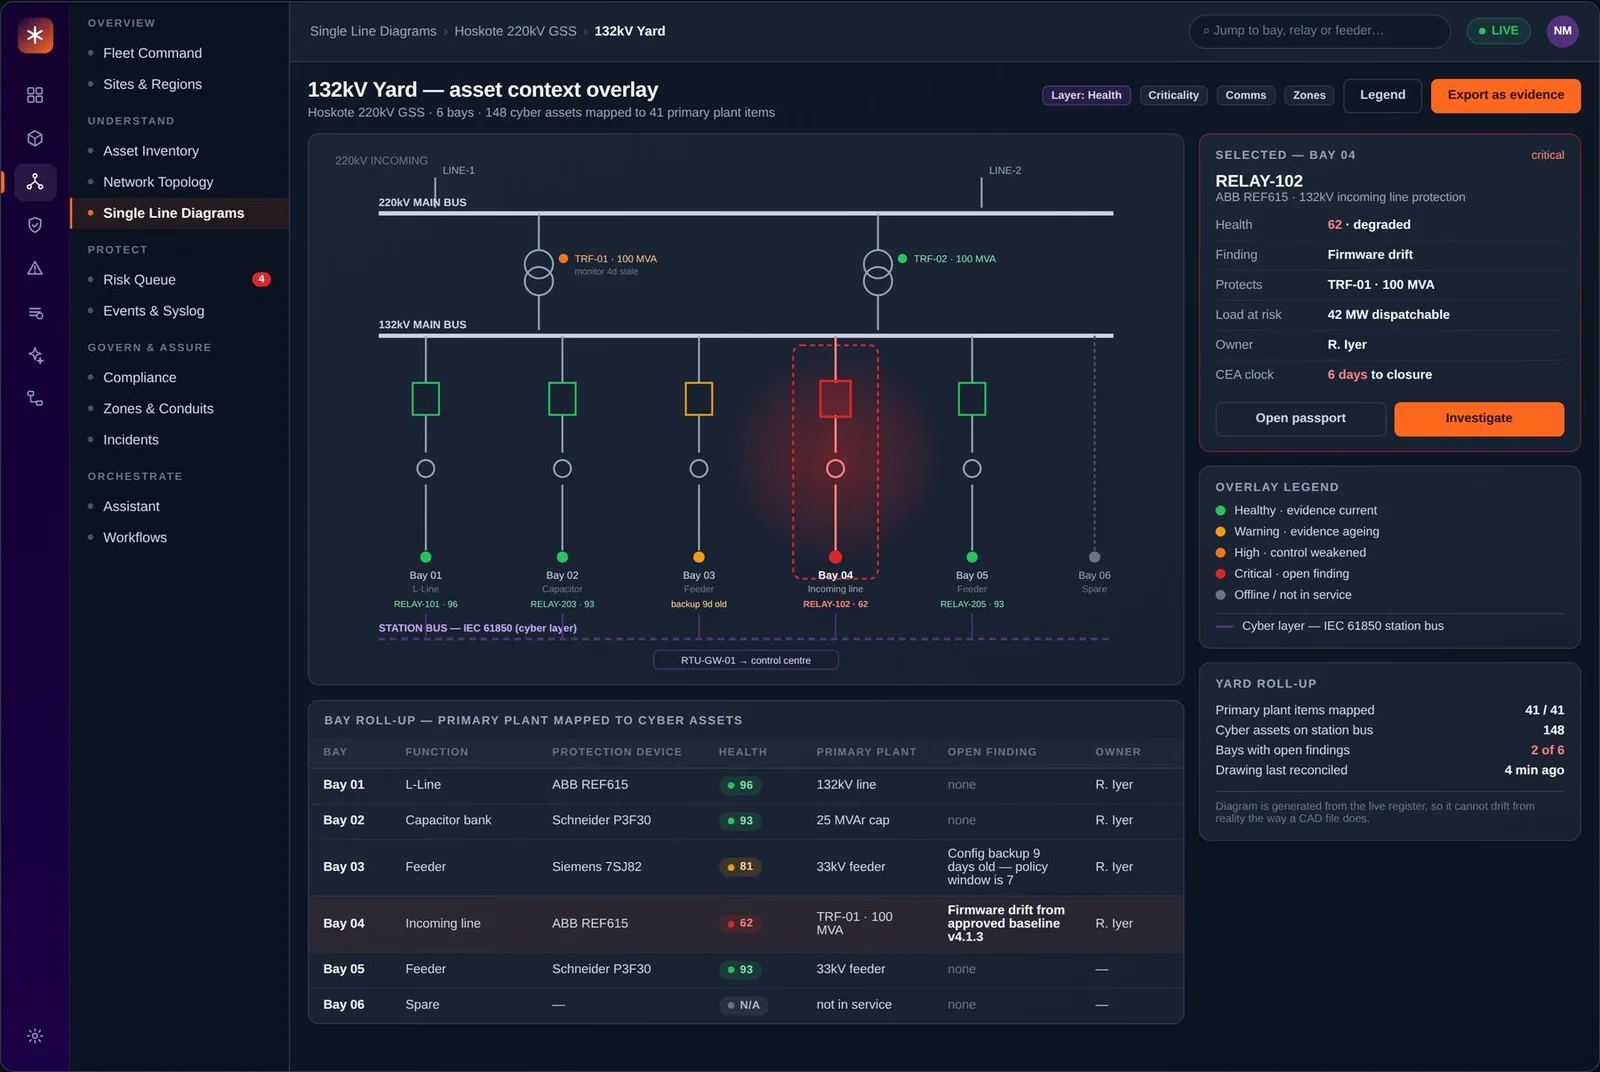
Protection engineers already think in bays and breakers. ASTRICS paints asset state, findings and consequence onto the diagram they use, so a finding on Bay 04 is a finding on Bay 04.
A passport for every relay
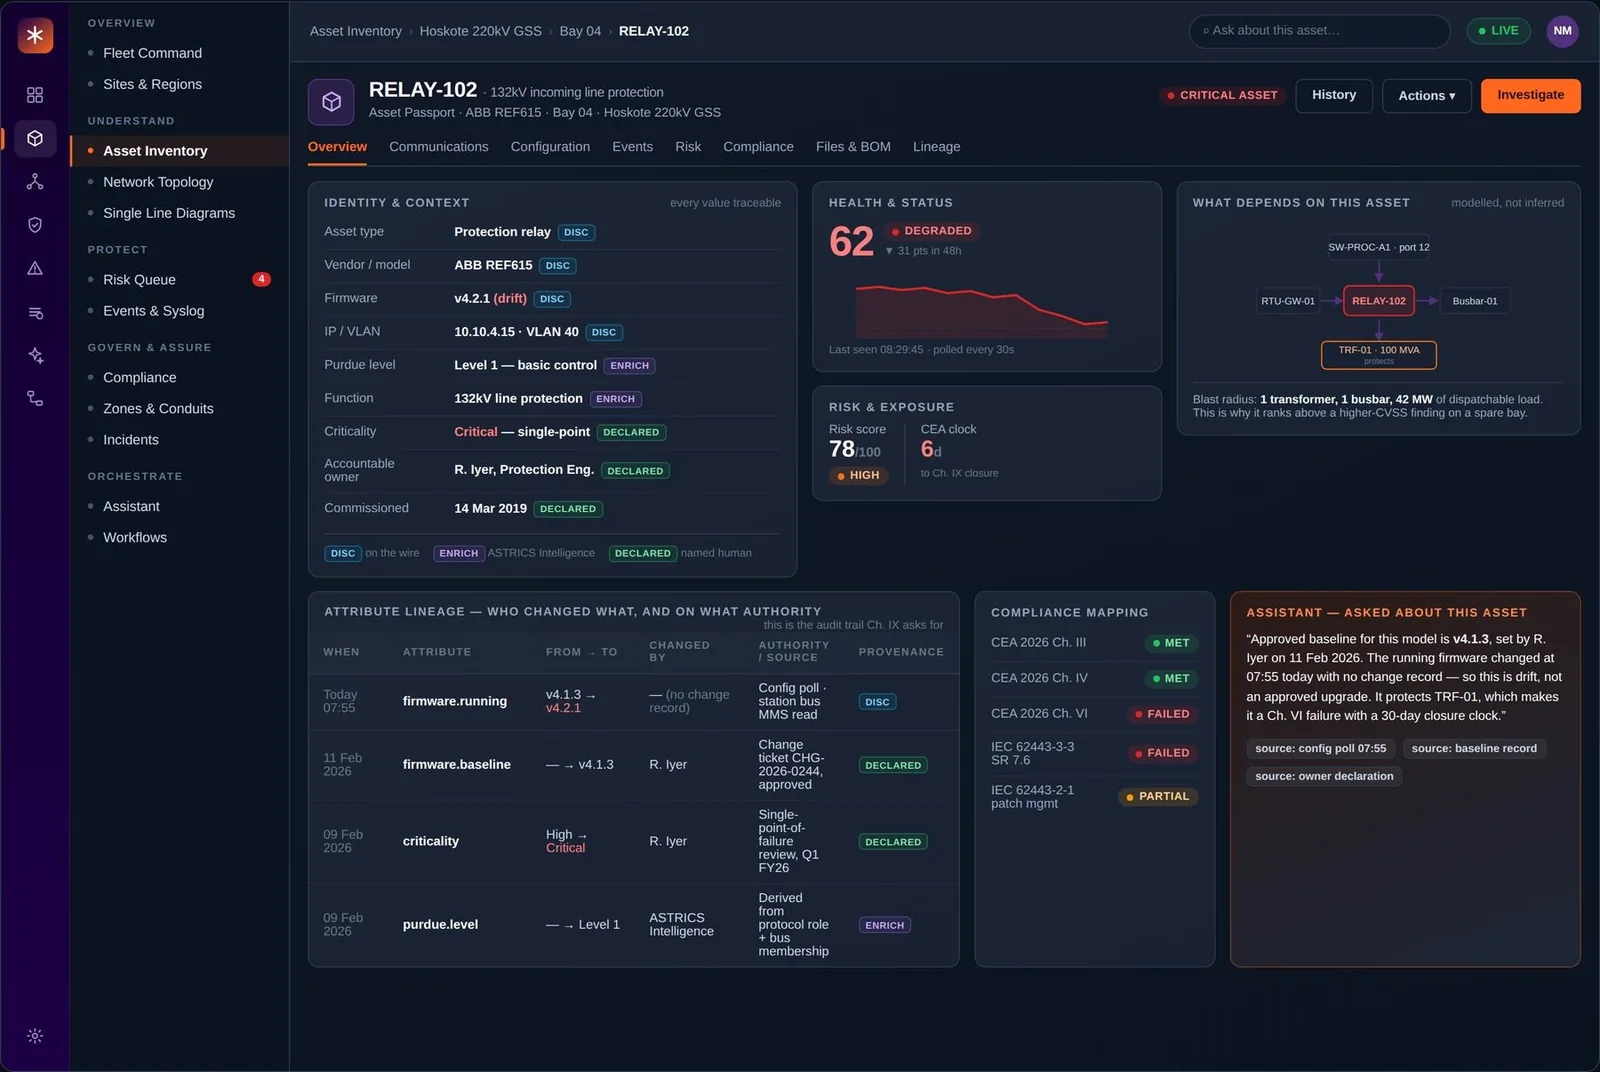
The Asset Passport holds firmware, settings lineage, communications and vendor access for each IED — the audit trail Chapter IX actually asks for.
Segmentation proven, not described
Declared trust levels are tested continuously against observed IEC 61850, IEC 104 and DNP3 flows. A conduit that appears on the wire but not in the design becomes a dated finding.
From six events to a submission
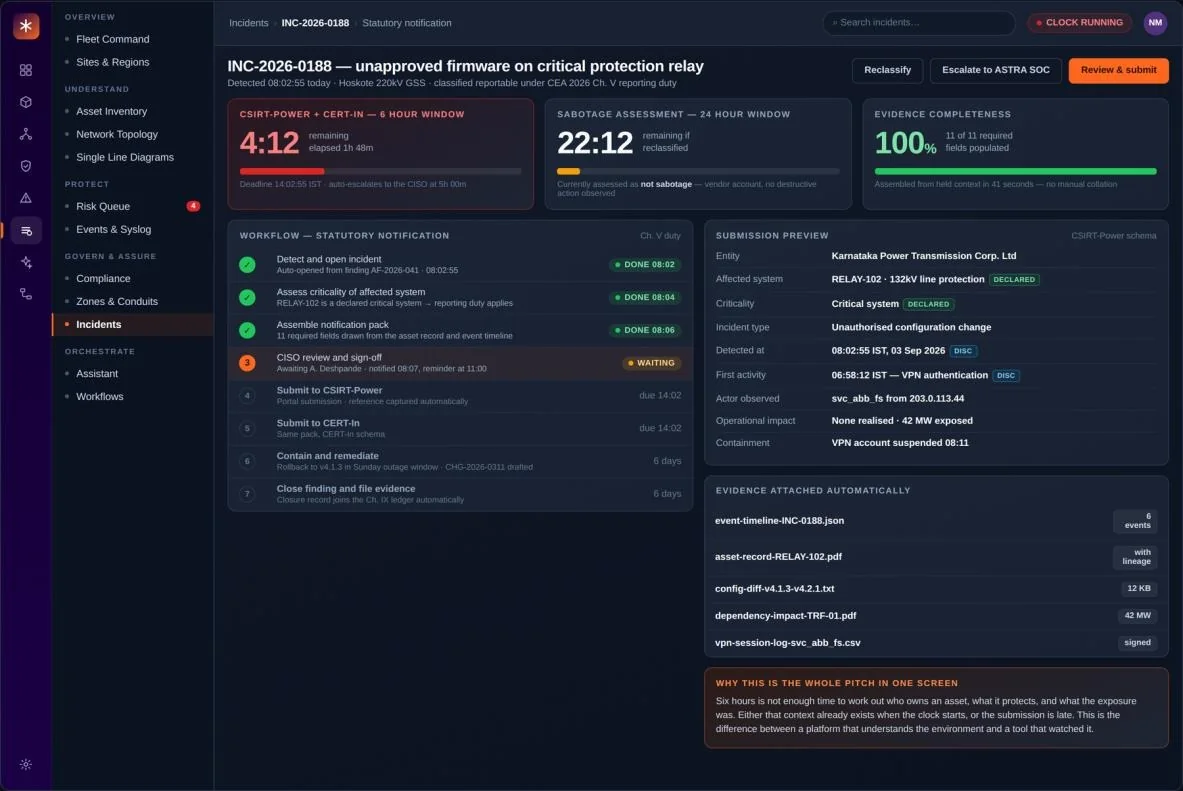
Native event and syslog collection correlates on the asset model, and the statutory incident workflow assembles the six-hour notification from context already held.
Single Line Diagram with Asset Context Overlay
The engineer's own drawing, alive. Cyber context is painted onto the layer operators already think in, so a finding reads as a bay, a transformer and a load.
Asset Passport
One asset's complete operational record — and every value on it carries its source, so an auditor can follow any figure back to where it came from.
Statutory Incident Response
CEA 2026 allows six hours to notify CSIRT-Power and CERT-In. The clock, the workflow and the submission all run inside the platform, assembled from context already held.
What operators askbefore they buy.
Straight answers, in the terms the regulation and the plant already use. Bring the rest to a walkthrough.
Does a small distribution licensee have a capacity threshold like generators do?
No. The 50 MW threshold in the regulation applies only to generating companies, captive plants and energy storage owners. Transmission licensees, distribution licensees and every load despatch centre are in scope regardless of size.
Our substations speak IEC 61850. Can ASTRICS read GOOSE and MMS without touching the protection?
ASTRICS observes traffic passively and builds the record from what it sees; writes to control devices are not a permission it can be granted — that path does not exist in the product. The confirmed protocol list for your estate is in the Technical Integration Guide, available on request.
Where do smart meters sit in the model?
Head-end systems, meter data management and the networks between them are modelled as the IT-to-OT boundary they are. ASTRICS shows where metering traffic meets distribution SCADA, ranks the assets on that boundary by consequence, and tests that the declared separation holds.
What does the regulation mean by a protected system?
Under section 70 of the Information Technology Act, the appropriate government can notify a computer resource that is critical information infrastructure as a protected system, which restricts access and raises penalties for unauthorised access. Regulation 5(29) requires an entity to give NCIIPC the information to identify such assets and to apply for notification within sixty days of identification.
See ASTRICS against your own environment.
Book a walkthrough with the ASTRICS team and bring one site's worth of questions.